

Cortex connects to many third-party vendors whose system interfaces frequently change. As a result, integration behavior or configuration steps may shift without notice. If you encounter unexpected issues, check with your system administrator or refer to the vendor’s documentation for the most current information. Additionally, integration sync times vary and are subject to scheduling overrides and timing variance.
- Display the latest scans and vulnerability data on entity details pages in Cortex
- Create Scorecards that track progress and drive alignment on projects involving Semgrep security data, allowing you to address and remediate vulnerabilities more efficiently
How to configure Semgrep with Cortex
Prerequisites
Before getting started:- Create an API token in Semgrep with
GET scan detailsandGET List code or supply chain findingspermissions.
Configure the integration in Cortex
- In Cortex, navigate to the Semgrep settings page:
- Click Integrations from the main nav. Search for and select Semgrep.
- Click Add configuration.
- Configure the Semgrep integration form:
- Alias: Enter an alias for this integration.
- API key: Enter the value of the API token you created in Semgrep.
- Organization ID: Enter your organization ID for Semgrep.
- Organization slug: Enter your organization slug for Semgrep.
- Click Save.
How to connect Cortex entities to Semgrep
Match entity names to Semgrep projects
By default, Cortex will use the Cortex tag (e.g.my-service) as the “best guess” for Semgrep projects. For example, if your entity name is “My Service” or your tag is my-service, then the corresponding project name in Semgrep should also be “My Service” or my-service.
If your Semgrep project names don’t cleanly match the Cortex entity name or tag, you can override this in the Cortex entity descriptor.
Editing the entity descriptor
Under thex-cortex-semgrep block in an entity’s YAML, you can define the projects you want based on the Semgrep project ID. For example:
Using the Semgrep integration
Viewing Semgrep information in Cortex
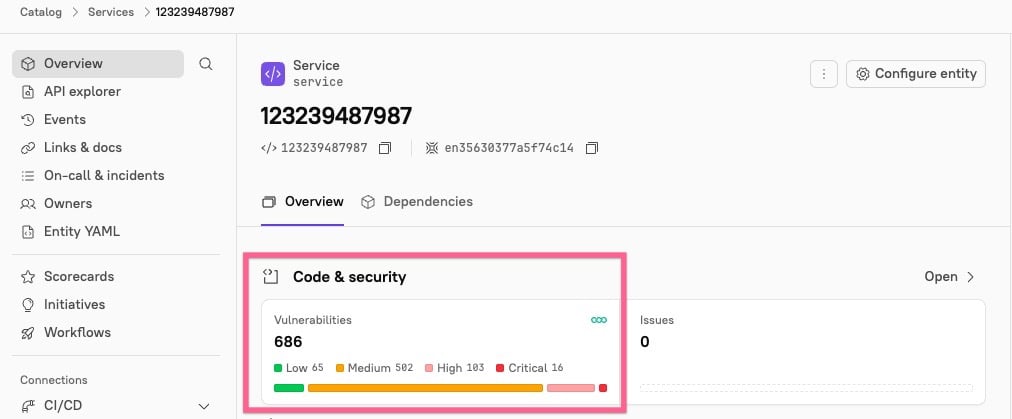
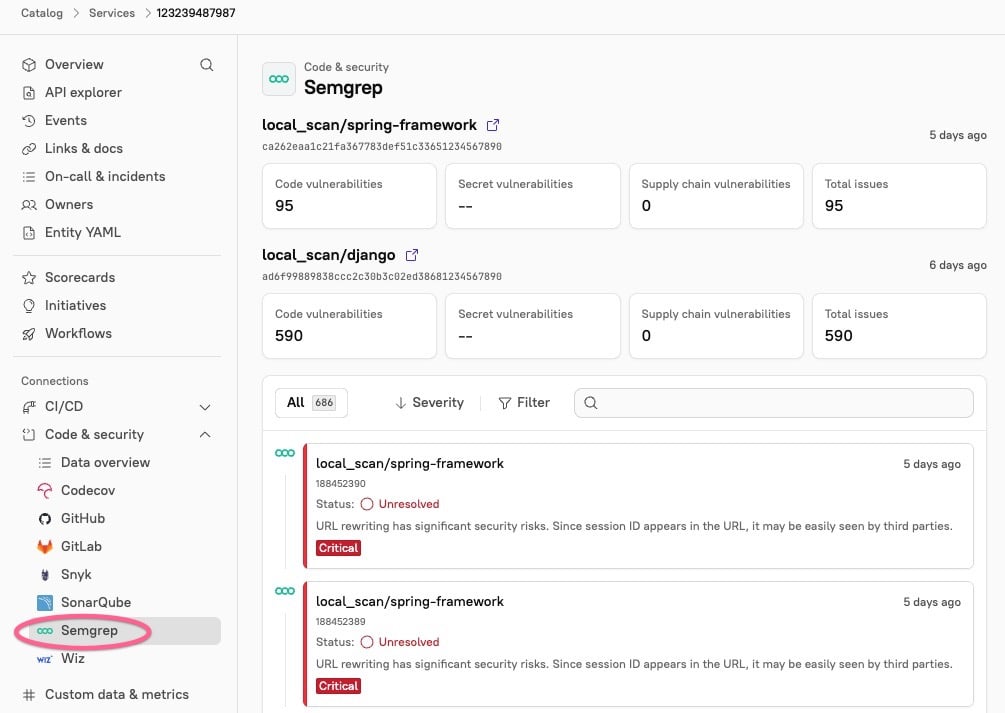
Semgrap vulnerabilities and scans appear on entity details pages:-
in the Code & security block in the entity’s overview:
-
in the entity’s sidebar in Code & security.
- This page contains scan results and vulnerability metrics from Semgrep. Click Filter at the top of the vulnerability list to filter by severity.
Scorecards and CQL
With the Semgrep integration, you can create Scorecard rules and write CQL queries based on Semgrep projects. See more examples in the CQL Explorer in Cortex.Check if Semgrep project is set
Check if Semgrep project is set
Check if entity has a registered Semgrep project in its entity descriptor.Definition: Setting a
semgrep (==/!=) null: BooleanExampleAn initial level in a security Scorecard might include a rule to make sure entities are associated with a Semgrep project:semgrep != null rule can also serve as a secondary check to confirm an entity is synced properly with Semgrep and is reporting frequently.List vulnerabilities
List vulnerabilities
List of Semgrep vulnerabilities by severity or type.Definition:
semgrep.vulnerabilities()ExampleYou can write a rule to verify an entity has fewer than 10 vulnerabilities:Get scan results for an entity
Get scan results for an entity
Get Semgrep scan results for an entity.Definition: You could write a rule to ensure an entity has had fewer than 10 new scans in the last week:
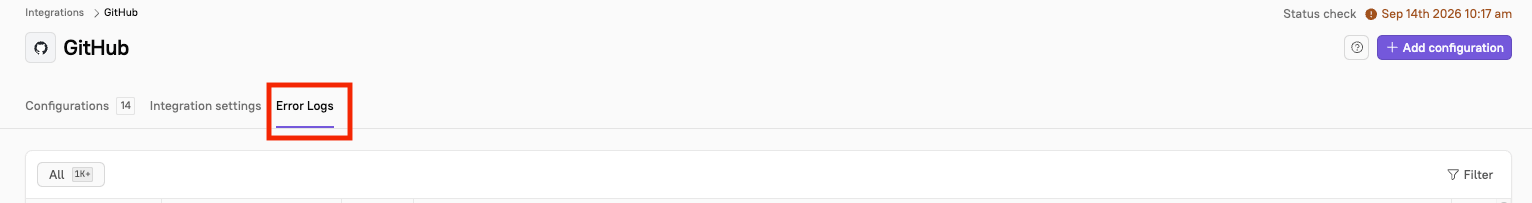
semgrep.scans()You could write a Scorecard rule to ensure an entity has fewer than 10 scans:View integration logs
This feature is available in Cortex cloud.
Still need help?↗
The following options are available to get assistance from the Cortex Customer Engineering team:- Email: help@cortex.io, or open a support ticket in the in app Resource Center
- Slack: Users with a connected Slack channel will have a workflow added to their account. From here, you can either @CortexTechnicalSupport or add a
:ticket:reaction to a question in Slack, and the team will respond directly.